Critical Check Point Login Flaw Exposes Management Servers to Root Takeover
Check Point has issued an urgent fix for CVE-2026-91843, a remotely exploitable buffer overflow that can grant root privileges before authentication. Administrators should deploy and verify the LivePatch...
Exploited Zero-Days and Perimeter Flaws Put Patch Triage Under Pressure
This week’s security picture is dominated by exploited Windows and Chrome zero-days, dangerous flaws in perimeter products and increasingly automated attack operations. Defenders need risk-based patch sequencing, exposure...
FortiGate Exploitation Campaign Plants PivotC2 Malware and Steals Network Credentials
Attackers are exploiting a critical Fortinet vulnerability to install a custom Node.js remote-access framework on exposed appliances. The campaign has reportedly compromised 178 devices and can harvest credentials,...
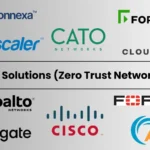
ZTNA in 2026: Ten Platforms Shaping Secure Access Beyond the Traditional VPN
A new 2026 market overview compares ten prominent zero-trust network access platforms for cloud, hybrid and remote environments. Buyers should look beyond feature checklists and test identity, device...
MikroTik RouterOS Flaw Under Active Attack Grants Unauthenticated Shell Access
Attackers are exploiting a RouterOS weakness that can reportedly provide unauthenticated shell access through exposed services, including SSH. MikroTik users should install the fixed releases now, audit every...
CISA Orders Rapid Action as Citrix NetScaler Flaw Is Exploited in the Wild
CISA has placed CVE-2026-8452 in its Known Exploited Vulnerabilities catalog following confirmed attacks against Citrix NetScaler products. The memory-safety flaw can disrupt critical gateway services, and organizations should...

ASUS Rushes Out Router Patch After Discovery of Unauthenticated Remote Command Execution Flaw
ASUS has issued firmware updates for a high-severity vulnerability, tracked as CVE-2026-13385, that could let remote attackers run arbitrary commands on widely deployed router models without authentication. Security...
State-Sponsored Hackers Exploit Cisco Catalyst SD-WAN Manager Zero-Day to Gain Root Access
A state-sponsored threat actor exploited zero-day CVE-2026-20245 in Cisco Catalyst SD-WAN Manager to gain root access via a malicious CSV upload. The multi-phase intrusion also leveraged two CVSS...