Microsoft Fixes CVSS 10 Azure AI Foundry Privilege-Escalation Flaw
Microsoft has remediated a maximum-severity authentication flaw in Azure AI Foundry that could allow an unauthenticated network attacker to gain elevated privileges. The cloud-side fix is complete, but...
Mass Scanning of Exposed Vite Servers Targets AWS and Azure Secrets
Attackers are automatically probing internet-accessible Vite development servers for environment files, cloud credentials and infrastructure secrets. F5 telemetry recorded about 32,000 raw events in August, highlighting the risk...
Cloud and SaaS Resilience Starts With Identity, Dependency Mapping and Tested Recovery
Cloud and SaaS adoption has replaced a clear network perimeter with overlapping identity and supplier dependencies. Organizations can limit cascading failures by mapping concentration risk, prioritizing exposed systems,...
ChatGPT Sandbox Isolation Flaw Created a Hidden Route for Cross-Account Data Theft
Researchers found that a shared internal package service could act as a covert communication channel between isolated ChatGPT containers. The proof of concept combined hidden instructions and connected-app...
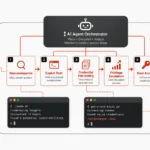
AI-Assisted Intruder Reaches Enterprise Root Access in Less Than 10 Hours
An attacker reportedly used frontier models and agentic frameworks to compress a complex enterprise intrusion into less than ten hours. The incident shows how exposed services, embedded secrets...
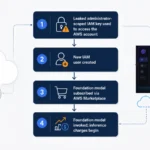
Leaked AWS Administrator Key Fuels Costly LLMjacking Through Bedrock and Marketplace
A leaked AWS IAM key with administrator privileges allowed an attacker to create a new identity, activate premium AI models and bill inference usage to the victim. The...
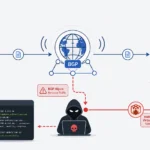
BGP Hijack Poisoned Virtualizor Updates and Put Hosting Servers at Root-Level Risk
A routing hijack diverted Softaculous infrastructure and enabled a malicious Virtualizor update to reach a small number of hosting servers. Because update packages lacked cryptographic verification, valid TLS...
Microsoft Confirms Entra ID Zero-Day Was Exploited Before the Fix Went Live
Microsoft has disclosed CVE-2026-69836, a maximum-severity deserialization flaw in Entra ID that attackers exploited in the wild before the company silently patched it server-side. There is no customer...