Ledger Confirms Rogue Hardware Chip Hidden Inside Crypto Wallets Tied to Over $86 Million in Losses
Ledger has confirmed that at least one hardware wallet sold through Southeast Asian reseller CryptoBilis contained an unauthorized physical implant, following reports of crypto theft that investigators estimate...
GhostAction Hijacks 346 GitHub Repositories to Harvest CI/CD Secrets
The GhostAction campaign used compromised maintainer accounts to inject credential-stealing GitHub Actions workflows into 346 repositories. The malicious automation collected CI/CD secrets and searched full Git histories, creating...
GlassWorm Hides Malware Inside VS Code Themes to Target Developer Workstations
GlassWorm operators used convincing VS Code theme extensions to conceal downloaders, encrypted JavaScript and blockchain-based payload routing. Developer teams should remove confirmed malicious packages and investigate hosts because...
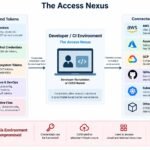
How a Single Poisoned Package Can Hand Attackers the Keys to Your Cloud
A new Qualys analysis ties together a string of 2025–2026 software supply chain campaigns — from the Shai-Hulud worm to malicious Ruby gems and Go modules — showing...
105 Minutes of Stolen Access Turned a Trusted npm Package Into a Multi-Stage Malware Loader
Attackers hijacked a maintainer account for just 105 minutes to slip a hidden loader into a popular npm package, abusing legitimate publishing infrastructure so the poisoned release carried...
Popular npm Package With Nearly 2 Million Weekly Downloads Hid Malware That Talks to Attackers Through Ethereum
Researchers at Checkmarx uncovered a supply-chain campaign hiding inside a widely used npm package that impersonates a legitimate data-structure library. Rather than infecting machines at install time, the...
BGP Hijack Poisoned Virtualizor Updates and Put Hosting Servers at Root-Level Risk
A routing hijack diverted Softaculous infrastructure and enabled a malicious Virtualizor update to reach a small number of hosting servers. Because update packages lacked cryptographic verification, valid TLS...
Hijacked Rust Crates With 244 Million Downloads Turned Into Malware Delivery Pipeline
A typosquatted Rust package quietly hijacked two popular crates, arrayref and append-only-vec, to run an infostealer during ordinary builds. The attack hid inside an automatically-executed build script, leaving...