FortiGate Exploit Opens Broadband Provider to Credential Theft and Network Pivoting
Researchers uncovered infrastructure indicating that attackers exploited a FortiGate SSL-VPN weakness during an intrusion targeting Thailand’s 3BB broadband provider. The operation combined perimeter access, privilege escalation, credential theft...
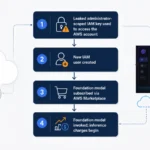
Leaked AWS Administrator Key Fuels Costly LLMjacking Through Bedrock and Marketplace
A leaked AWS IAM key with administrator privileges allowed an attacker to create a new identity, activate premium AI models and bill inference usage to the victim. The...
BREEZE COMET Hackers Use AI-Written Tools to Speed-Run Brazilian Bank Fraud
Google Cloud researchers detail how the financially motivated BREEZE COMET group has spent two years infiltrating Brazilian banks and retailers, combining social engineering and rogue hardware with generative-AI-assisted...
Cyber Incident Halts Small UK Power Plant for Four Days as Attribution Remains Unclear
A cyber incident reportedly stopped a small British peaking power plant for roughly four days without disrupting customers or the wider grid. Officials confirmed the event, while key...
FBI Dismantles Chinese State-Sponsored Botnet That Powered a Global Hacking Platform
The FBI and Department of Justice have seized the domains behind QScan and QTRouter, a pair of linked platforms that a Chinese state-sponsored group allegedly used to hijack...
Iran-Linked Hackers Knocked a UK Power Plant Offline for Four Days in a First-of-Its-Kind Attack
A small UK energy generator was forced completely offline for four days last month in what officials describe as the first successful cyberattack to shut down a British...
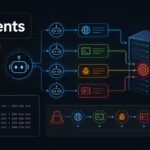
Chinese Threat Group Automates Web Server Attacks at Scale Using AI Agents, Cisco Talos Warns
Cisco Talos has tracked a Chinese-speaking group known as UAT-10147 using AI-generated scripts and playbooks to automate reconnaissance and exploitation across roughly 170,000 URLs. The campaign hit government,...
How T-Mobile’s Security Team Cut a Cable to Physically Kick Salt Typhoon Off Its Network
Newly reported details describe how T-Mobile's security team tracked Chinese state-linked hackers from Salt Typhoon to a compromised router at a third-party data center in 2024 — and...