FortiGate Exploit Opens Broadband Provider to Credential Theft and Network Pivoting
Researchers uncovered infrastructure indicating that attackers exploited a FortiGate SSL-VPN weakness during an intrusion targeting Thailand’s 3BB broadband provider. The operation combined perimeter access, privilege escalation, credential theft...
Malicious Twitch Extension Leaks OAuth Tokens From 30,000 Browser Users
A Twitch helper extension installed by about 30,000 Chrome and Firefox users was found sending active account tokens through operator-controlled servers. The incident shows how a seemingly convenient...

Phishing Campaign Builds Fake Login Pages Inside Browsers After Trusted Microsoft Redirects
A phishing campaign chains DocuSign-themed calendar invitations, Microsoft redirects and browser blob URLs to display credential-stealing pages assembled in local memory. The method reduces reliance on a conventional...
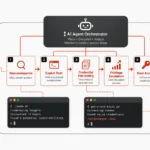
AI-Assisted Intruder Reaches Enterprise Root Access in Less Than 10 Hours
An attacker reportedly used frontier models and agentic frameworks to compress a complex enterprise intrusion into less than ten hours. The incident shows how exposed services, embedded secrets...
Phishing Campaign Chains Google Services to Conceal Credential Theft
A phishing operation is routing victims through legitimate Google services before sending them to personalized credential traps or unauthorized ScreenConnect installers. The technique weakens domain-reputation defenses and hides...
QR-Code Phishing Reaches Record Levels as Attackers Shift Credential Theft to Phones
ESET says QR-code phishing accounted for about 11% of detected phishing email in the first half of 2026, with roughly 100,000 detections per month. By moving victims from...
TukTuk Malware Gives Ransomware Crews Cross-Platform Control and EDR-Killing Tools
Researchers recovered a previously undocumented command-and-control framework linked to the Gentlemen ransomware ecosystem. TukTuk supports Windows and Linux agents, credential prompts, screen capture, remote commands, and preparation for...
Mirage2FA Phishing Kit Hijacks Microsoft 365 Sessions at 3,500+ Organizations, Sidestepping MFA Entirely
A phishing-as-a-service kit called Mirage2FA has compromised thousands of Microsoft 365 accounts by stealing live session cookies through an adversary-in-the-middle proxy, letting attackers walk past passwords and MFA...