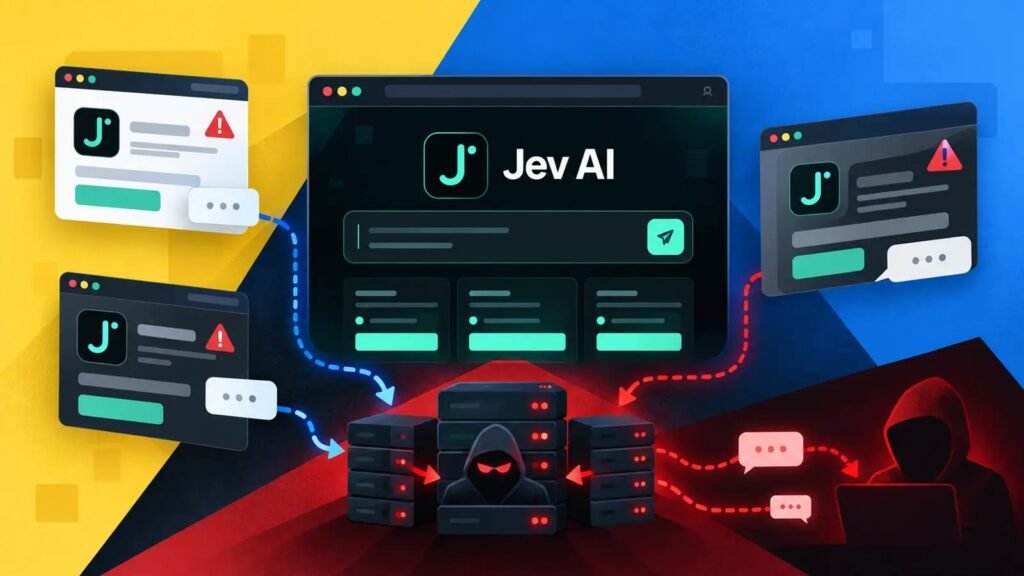
New AI models tend to attract two crowds the moment they launch: early adopters, and opportunists looking to cash in on the confusion. Researchers Dion Fieret and Lucas Hop of Eye Security have documented the latter in detail, uncovering a network of fraudulent storefronts built around Jev, an AI model that returns decisions rather than written text, just days after its official September 15, 2026 debut.
Real API, Inflated Price Tag
These aren’t fake AI products in the sense of returning garbage output — that’s part of what makes them effective. The storefronts quietly forward every request to the genuine Jev API while charging users far more than the real service costs. The official API prices input tokens at $0.042 per million. The knockoff sites, by contrast, run monthly subscription tiers ranging from $0.247 to $0.483 per million tokens — a markup of roughly 6 to 11.5 times the legitimate rate. Annual plans are also on offer, but they require payment upfront, locking customers in before they have much chance to notice the gap.
Outranking the Real Developer
Search visibility is part of the scam’s design. Several of these lookalike domains rank prominently for searches like “Jev AI,” in some cases appearing above the official developer’s own site. The storefronts aren’t crude either — they come complete with interactive playgrounds, documentation pages, pricing tables, and fully functional checkout flows. Two of the malicious domains were registered just 11 hours apart on September 18, 2026, only three days after Jev’s launch, suggesting the operators were watching closely and moved fast.
The Bigger Problem: Where the Prompts Actually Go
Beyond the pricing, there’s a more serious concern buried in the plumbing. Eye Security traced one storefront’s traffic through an intermediary application hosted on Railway, sitting behind Cloudflare, before it ever reached the official Jev API. As the researchers put it, users “could pay up to 11.5 times the official rate while sending their prompts through servers they do not control.” There’s no service agreement disclosing how that middleman handles submitted prompts or any sensitive business information they might contain — which means anyone using one of these storefronts for real work has effectively handed their data to an unknown third party with no accountability.
Not a One-Off Scam, But a Template Business
The Jev impersonation turned out to be one piece of a larger, more mechanical operation. Researchers found that one storefront belonged to a network of six coordinated sites, all built from identical code templates and simply rebranded whenever a new AI, music, or video service started trending — six variants appeared within just 18 days. The sites share the same standardized pricing tiers ($29, $49, and $98 monthly plans), the same welcome-credit and daily-reward gimmicks, and the same countdown timers manufacturing urgency around “annual savings” that quietly reset every day. Certificate transparency logs turned up roughly 670 newly registered domains containing the word “Jev” within just eight days of the model’s launch — about double the normal background rate of registrations tied to a new model’s name.
How to Spot One Before You Pay
Eye Security’s researchers flagged a consistent set of warning signs across these sites: legal documents with dates that shifted during the course of the investigation, no clear identification of the company actually operating the service, and no disclosure of how user data is handled. Their recommendations for avoiding this kind of scam are straightforward:
- Get access links directly from the model developer’s official announcements, not from search results.
- Compare the advertised per-token price against the vendor’s published official pricing.
- Check how recently the domain and its TLS certificate were registered.
- Look for a clearly named legal entity in the terms of service, not a vague or missing one.
- Confirm, in writing, who actually processes and stores submitted data before sending anything sensitive.
Known Malicious Domains
Eye Security’s report lists 34 suspicious domains tied to this campaign, including confirmed malicious sites such as jev-ai[.]pro, jevtypesafeai[.]com, jev-agent[.]org, jev-agent[.]com, jevapi[.]pro, and jevmodel[.]org, along with a number of additional domains built from the same storefront template. The researchers note they haven’t confirmed malware delivery through these sites — the immediate risks are financial overcharging and unclear handling of submitted data, both serious enough on their own for anyone routing real prompts through a storefront they haven’t verified.
Leave a Reply
You must be logged in to post a comment.