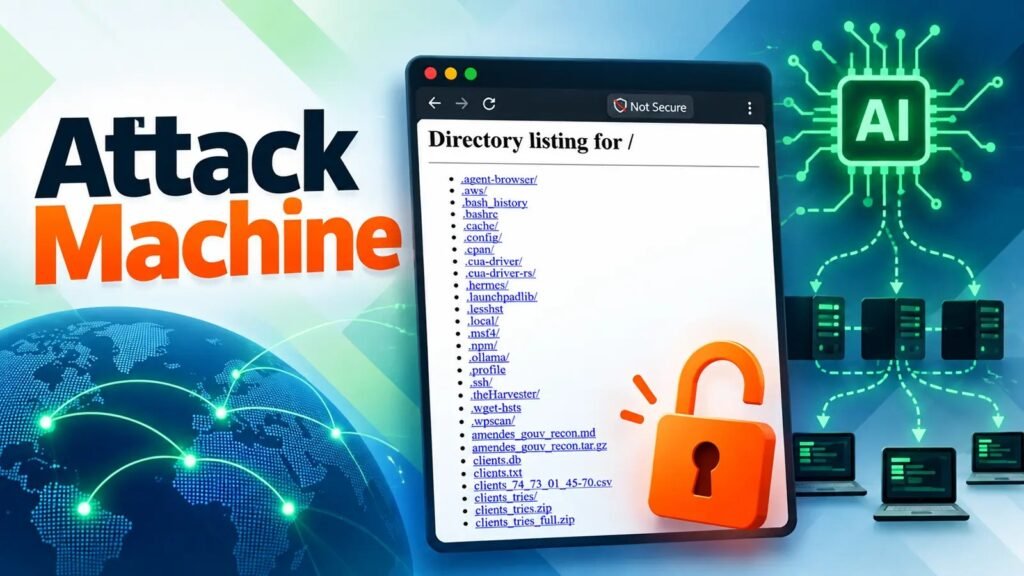
Threat intelligence researchers at ThreatMon have gotten an unusually clear look inside an active cybercrime operation, after a group linked to the handles Blackhatsect0r and DXQRTXX left one of its own servers sitting open on the internet without authentication. What the researchers found wasn’t just a pile of stolen data — it was the full operational blueprint of an automated attack platform, including the source code, target lists, and internal chat logs the group used to run it.
What Was Sitting on the Open Server
The exposed system contained 16,415 credential records and roughly 498,000 target URLs earmarked for future attacks, alongside source code, chat transcripts, fraud notes, and internal exploitation write-ups. Among the target list were 449 subdomains belonging to French government entities, pointing to a deliberate, systematic effort to map state infrastructure. In an ironic twist, the group’s own Telegram conversations show members discussing operational security even as the files they left exposed laid out their entire operation for anyone who found them.
An Attack Pipeline Built for Scale, Not One-Offs
Rather than running attacks by hand, the group built persistent infrastructure that paired broad automated discovery with focused, human-led follow-up. The system’s backbone was a command-and-control framework written in Go, paired with a Python-based discovery engine that continuously scanned for vulnerable systems. That engine pulled from certificate transparency logs, DNS records, and repeated subdomain enumeration to keep generating fresh candidate targets. ThreatMon’s analysis confirms this was automated reconnaissance at scale rather than proof of an AI directing individual intrusions, though earlier reporting has tied this group to AI-assisted workflows elsewhere in its operations.
Two Campaigns, Neither Relying on a Zero-Day
The leaked files revealed two significant targeted campaigns, and what stands out is how ordinary the underlying weaknesses were. The first went after France’s ANTAI traffic-fine payment platform, where the attackers picked apart browser-delivered application code, attempted to forge authentication tokens, probed request handling, and tried to enumerate payment records — a case study in why signing material must never be exposed to the client side. The second campaign targeted a cryptocurrency exchange after the group discovered a readable environment configuration file, which they used to attempt privilege escalation, review account balances, and prepare fraudulent withdrawals.
Neither intrusion depended on a novel exploit. Both traced back to exposed configuration files, hardcoded secrets, and applications leaking more than they should to the browser — mistakes that are entirely preventable.
From Data Broker to Tool Vendor
The group’s Telegram channel first went active in May 2026, initially trading in stolen databases. By mid-August, the operation pivoted after subscribers voted in favor of distributing offensive tools rather than continuing to share databases — a shift that suggests the crew is moving from targeting individual victims toward supplying capability to a wider pool of attackers. Internal communications show coordination among several distinct handles, each apparently responsible for a different piece of the operation, consistent with a small, organized team rather than a lone actor.
The Real Lesson: Basic Hygiene Still Matters
What makes this exposure notable isn’t just what it revealed about one group — it’s the reminder that automated discovery tools like the one this crew built are actively hunting for exactly the kind of misconfigurations that let both of its campaigns succeed. Security teams should treat this as a prompt to review their own exposure:
- Remove configuration files and version-control directories from publicly accessible web paths.
- Keep token-signing keys and other cryptographic material strictly server-side, never delivered to the browser.
- Replace weak or default credentials and rotate any secret that may have been exposed, even briefly.
- Watch logs for repeated, systematic reconnaissance patterns rather than isolated probes.
- Restrict access to administrative interfaces and monitor external-facing infrastructure continuously.
- Investigate matching indicators of compromise quickly and preserve logs for follow-up analysis.
As this case shows, sophisticated tooling isn’t what usually gets an attacker in the door — a stray configuration file or an overlooked environment variable is. Organizations that routinely check for that kind of exposure and close it quickly shrink the window that automated crews like this one depend on.
Leave a Reply
You must be logged in to post a comment.