Inside the Supply Chain Playbook Turning Trusted Software Updates Into Credential Thieves
A new ReversingLabs report ties together the S1ngularity, Shai-Hulud, and TeamPCP/Trivy supply chain incidents, showing how stolen maintainer tokens and compromised CI pipelines let attackers push credential-stealing code...
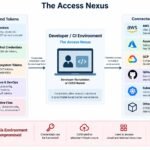
How a Single Poisoned Package Can Hand Attackers the Keys to Your Cloud
A new Qualys analysis ties together a string of 2025–2026 software supply chain campaigns — from the Shai-Hulud worm to malicious Ruby gems and Go modules — showing...
105 Minutes of Stolen Access Turned a Trusted npm Package Into a Multi-Stage Malware Loader
Attackers hijacked a maintainer account for just 105 minutes to slip a hidden loader into a popular npm package, abusing legitimate publishing infrastructure so the poisoned release carried...

Grafana GitHub Breach: TanStack npm Supply Chain Attack Leads to Source Code Theft and Ransom Demand
Grafana Labs has confirmed a ransomware-linked breach of its GitHub environment traced to the TanStack npm supply chain compromise. Attackers exfiltrated internal source code repositories and issued a...

art-template npm Package Backdoored to Deliver iOS Browser Exploit Kit via Supply Chain Attack
Attackers hijacked the widely-used art-template npm library by taking over its maintenance, then injected a sophisticated iOS browser exploit kit that silently targeted Safari users on vulnerable devices...