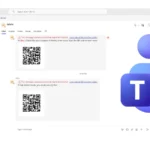
Microsoft Teams Adds Post-Delivery Warnings for Malicious QR-Code Links
Microsoft Defender for Office 365 is extending Teams protections to inspect URLs encoded in QR images and warn users when a destination is malicious. The rollout improves post-delivery...
Microsoft Teams to Add Third-Party Deepfake Detection as Synthetic-Media Attacks Escalate
Microsoft plans to roll out synthetic audio and video detection in Teams starting November 2026, routing meeting media through certified third-party providers to flag possible deepfakes. The move...

Phishing Campaign Builds Fake Login Pages Inside Browsers After Trusted Microsoft Redirects
A phishing campaign chains DocuSign-themed calendar invitations, Microsoft redirects and browser blob URLs to display credential-stealing pages assembled in local memory. The method reduces reliance on a conventional...
Microsoft Investigates Windows Teams Startup Failures as Users Turn to Web and Mobile
Some Windows users are seeing Microsoft Teams fail to open or take up to two minutes to load. Microsoft is gathering client logs under incident TM1466820, while web...
Fake Teams Help-Desk Calls Turn Remote Support Into a Path Toward Domain Control
A campaign dubbed Spring Ring used external Microsoft Teams accounts and convincing help-desk calls to push remote-access tools and malware. In some cases, the attackers progressed toward SMB...
Microsoft Is Giving Teams Admins a Single Dashboard to Catch Phishing and Malware in Chats
Microsoft is rolling out a new Security Detection Report inside the Teams admin center that consolidates impersonation attempts, malicious links, and dangerous file types into one exportable dashboard....

DragonForce Ransomware Abuses Microsoft Teams TURN Relay to Hide Malicious C2 Traffic
Symantec researchers have discovered that DragonForce ransomware actors used a novel Go-based backdoor called Backdoor.TURN to route C2 communications through Microsoft Teams TURN relay servers — the first...

Hackers Are Calling You on Microsoft Teams Pretending to Be IT Support — How to Detect and Stop the Attack
Threat actors are systematically abusing Microsoft Teams' external collaboration features to impersonate IT helpdesk staff, convincing employees to grant remote access and install malware. Black Basta ransomware affiliates...