HEAVYGRAM Backdoor Uses Telegram to Spy on Journalists and Iranian Dissidents
Researchers have expanded the known scope of HEAVYGRAM, a Windows surveillance backdoor that uses Telegram bots and groups for command and control. The campaign targets journalists and Iranian...
Fake Job Interviews Deliver NodeRabbit and PollCat Malware to Software Developers
An Iran-linked group tracked as Mirage Kitten (UNC1549) is posing as recruiters on LinkedIn to trick developers into running malicious take-home coding tests. The booby-trapped projects deploy two...
Cyber Incident Halts Small UK Power Plant for Four Days as Attribution Remains Unclear
A cyber incident reportedly stopped a small British peaking power plant for roughly four days without disrupting customers or the wider grid. Officials confirmed the event, while key...
Iran’s Cyber Playbook Shifts From Loud Attacks to Patient, Long-Term Access
A new SentinelOne assessment finds Iran-linked hacking groups increasingly favor quiet, persistent access over destructive attacks, planting footholds in cloud accounts, IT suppliers, and industrial systems that could...
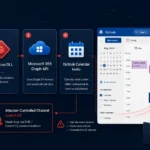
HOLLOWGRAPH Malware Turns Microsoft 365 Calendars Into a Covert Spy Channel
Group-IB has uncovered HOLLOWGRAPH, a stealthy malware component that hides its command-and-control traffic inside Microsoft 365 calendar invites dated decades in the future. The tool shows technical overlap...
Cavern Manticore: Iranian-Linked APT Abuses SysAid RMM and DLL Sideloading to Deploy Modular C2 Framework
A newly identified Iranian-linked group, Cavern Manticore, is abusing the SysAid RMM platform and DLL sideloading via WinDirStat to deploy a modular C2 framework against Israeli organizations. Check...

CyberAv3ngers: Iran-Linked IRGC Hackers Target Rockwell PLCs Across U.S. Critical Infrastructure
A joint CISA advisory warns that Iran-linked CyberAv3ngers (IRGC-CEC) are actively exploiting internet-exposed Rockwell Automation PLCs across U.S. water, energy, and government sectors. Over 5,200 devices are publicly...

MuddyWater-Linked APT Campaign Scanned 12,000+ Systems Before Striking Middle East Critical Infrastructure
Iran-linked threat group MuddyWater is behind a sophisticated espionage campaign that scanned over 12,000 systems in the Middle East before stealing passport records and payroll data from an...