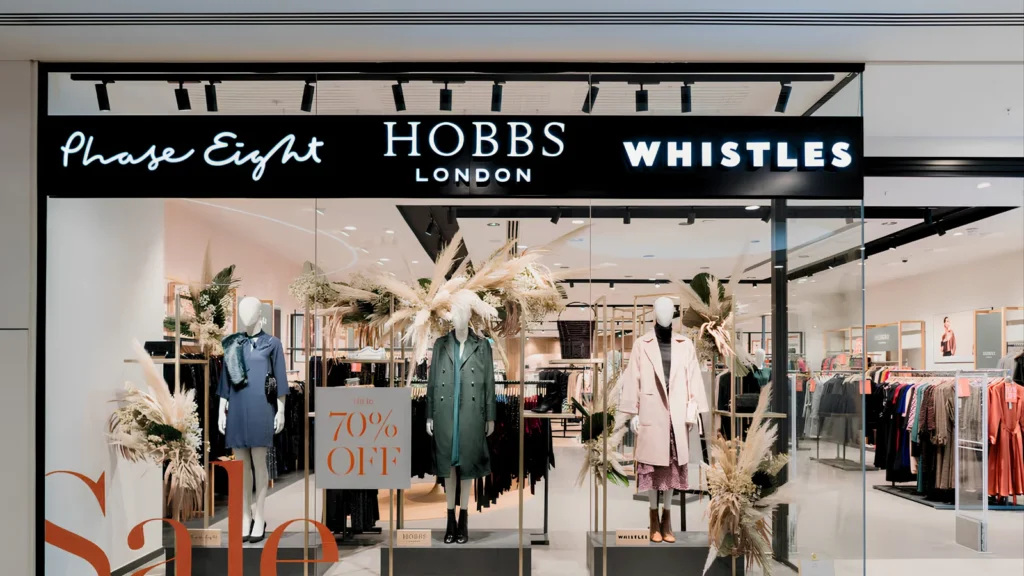
Stores Stay Open, But Systems Go Down
The Foschini Group (TFG), the South African retail conglomerate, has confirmed that a cyberattack disrupted IT systems supporting three of its UK fashion brands: Phase Eight, Hobbs, and Whistles. The company detected the intrusion on October 11, 2026, and disclosed it to shareholders two days later. According to TFG’s shareholder statement, physical stores for the affected brands have continued trading throughout the disruption, even as several backend systems remain unavailable.
Two other UK brands under TFG’s umbrella, Inside Story and White Stuff, were not affected by the incident. TFG’s operations in Africa and Australia also escaped impact entirely, because those regions run on separate IT infrastructure from the UK business. The confirmed disruption therefore appears limited to part of TFG’s UK retail operations rather than the group’s global footprint.
Incident Response Underway
TFG says it activated its incident response and business continuity plans as soon as the attack was discovered, and has brought in external cybersecurity specialists to help contain it. UK regulators and other relevant authorities have also been notified. The company’s investigation into whether personal or other sensitive customer information was accessed or stolen is still ongoing.
What Customers Can Expect
For shoppers, the practical impact includes some unavailable website functions and delays affecting orders placed on or after October 11. TFG has asked customers not to resubmit any delayed orders, and says purchases made before that date should process and ship normally.
On the question of payment security, TFG told customers that a third-party provider handles its payment processing, and that based on its investigation so far, the company has “no reason to believe that payment information is at risk.” Importantly, TFG has not ruled out that other categories of customer data may have been exposed, and says it will directly notify any customers found to be affected once its investigation concludes.
Key Details Still Undisclosed
TFG has not publicly identified who is responsible for the attack, how the attackers gained initial access, or whether ransomware played a role. The company has also not given a timeline for when disrupted systems will be fully restored. Without more technical detail, it remains unclear exactly which applications were affected across the three brands or how access was shared, or isolated, between them.
Not TFG’s First Brush With Disruption This Year
The company’s June financial results referenced an earlier incident affecting a key online concession partner, one of several pressures weighing on its UK business, a portfolio that saw adjusted operating profit fall 65.4%, excluding brand impairment and acquisition costs. That earlier figure reflects broader financial headwinds and should not be mistaken for the cost of October’s attack specifically.
Part of a Difficult Year for UK Retail
TFG’s disclosure adds to a string of high-profile cyber incidents affecting UK retailers in 2026, including the Marks & Spencer attack that disrupted payment and click-and-collect services, and a supplier-side data breach affecting Harrods customers. There is no indication the TFG incident is connected to either of those cases, but the pattern underscores how attractive retail IT environments, with their mix of point-of-sale systems, e-commerce platforms, and third-party integrations, have become for attackers.
What Comes Next
For now, the central open questions are how attackers got in, what data, if any, was taken, and when TFG’s UK brands can fully restore normal operations. Security researchers note that visibility gaps like these are common in the early days of an incident response, and that alerts alone often cannot reconstruct a full attack timeline without deeper forensic work.
- Customers of Phase Eight, Hobbs, and Whistles should watch for direct communication from TFG regarding their own data.
- Treat unsolicited messages referencing the incident, especially those asking for account or payment details, with caution.
- Expect possible delays on orders placed on or after October 11 and avoid resubmitting them.
Leave a Reply
You must be logged in to post a comment.