UAC-0099 Refines MATCHBOIL Malware With Cloudflare-Hidden Servers to Hit Ukrainian Organizations
ESET researchers have detailed how the UAC-0099 threat group has evolved its MATCHBOIL downloader with Cloudflare-concealed command servers, stronger code obfuscation, and anti-analysis checks. Victims span transportation, manufacturing,...
Compromised Tensorlake npm Release Spreads Shai-Hulud Worm Through Developer Systems
A malicious Tensorlake npm release executed during installation, harvested developer and cloud secrets, and used worm-like techniques to threaten downstream projects. Teams that installed version 0.5.144 should treat...
Fake Rabby and OKX Wallet Clones Found Stealing Crypto Seed Phrases via Firefox Add-ons
Researchers at Socket.dev uncovered 16 malicious Firefox extensions posing as Rabby Wallet and OKX Wallet that quietly captured recovery phrases and private keys and sent them to attacker-controlled...
Fake Cloudflare Verification Pages Used to Push LUNEXSTEALER Malware on 100+ Hacked Sites
Ukraine's CERT-UA is tracking a campaign, dubbed UAC-0277, that has compromised more than 100 legitimate websites to show visitors a convincing but fake Cloudflare verification screen. Clicking through...
GlassWorm Hides Malware Inside VS Code Themes to Target Developer Workstations
GlassWorm operators used convincing VS Code theme extensions to conceal downloaders, encrypted JavaScript and blockchain-based payload routing. Developer teams should remove confirmed malicious packages and investigate hosts because...
Fake CAPTCHA Prompts Are Hiding Malware in Your Browser Cache, Microsoft Warns
Microsoft Threat Intelligence has uncovered a ClickFix variant that pre-stages a disguised VBScript payload inside the browser cache before a victim ever pastes a command into the Windows...
Fake Zoom and PDF Installers Deploy Dual Remote-Control Tools on Business PCs
A phishing campaign disguises legitimate MSP360 remote-management software as Zoom installers, PDF readers and business documents. Once installed, it adds ScreenConnect as a second access channel and delivers...
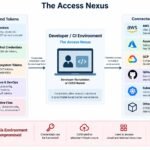
How a Single Poisoned Package Can Hand Attackers the Keys to Your Cloud
A new Qualys analysis ties together a string of 2025–2026 software supply chain campaigns — from the Shai-Hulud worm to malicious Ruby gems and Go modules — showing...