The Payroll Pirates: a malvertising and layered attack infrastructure
The “Payroll Pirates,” as Check Point researchers have dubbed them, represent a particularly insidious threat – a coordinated campaign targeting payroll systems, credit unions, and trading platforms across...
SmartApeSG: the persistent evolution of a ClickFix-based RAT campaign
The SmartApeSG campaign, previously identified by aliases like ZPHP and HANEY MANEY, continues to demonstrate a remarkable capacity for adaptation, moving beyond initial tactics of deceptive browser update...
Sophos exposes massive GitHub campaign distributing backdoored malware
A sophisticated malware campaign targeting hackers, gamers, and cybersecurity researchers has been uncovered on GitHub, leveraging fake exploits, game cheats, and open-source tools to distribute backdoors. The operation,...
Debunking OrbitShade: AI-Driven misinformation in Cyber Threat Intelligence
The recent public report dated April 29, 2025, alleging the existence of a state-sponsored malware named OrbitShade targeting satellite infrastructure appears to be a fabricated narrative likely generated...
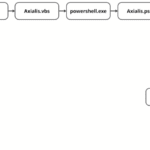
Anatomy of the Winos 4.0 campaign
The Winos 4.0 campaign, as dissected by Rapid7, exemplifies the evolving sophistication of contemporary malware operations targeting Chinese-speaking environments. This campaign leverages a multi-layered loader architecture, dubbed the...
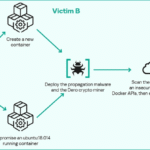
Dero miner container infection campaign
The recent campaign uncovered by Kaspersky, involving the Dero cryptocurrency miner spreading through containerized Linux environments by exploiting exposed Docker APIs, represents a sophisticated and highly automated threat...
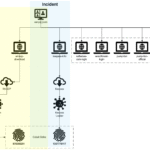
Trojanized KeePass campaign: novel loader and credential theft in ransomware operations
A recent investigation by WithSecure’s Threat Intelligence team has uncovered a sophisticated malware campaign leveraging a trojanized version of the open-source password manager KeePass. This operation, active for...
Sophisticated npm malware campaign exploits Cross-Ecosystem typosquatting
A coordinated malware operation targeting npm employs cross-ecosystem typosquatting to mimic popular libraries from Python, Java, C++, and .NET ecosystems. Attackers uploaded packages like beautifulsoup4 (masquerading as Python’s...