Inside GhostCode: The Phishing Kit That Turns MFA Approval Into Account Takeover
A newly identified phishing kit called GhostCode hijacks Microsoft 365 accounts by abusing the OAuth device-code sign-in flow, letting victims unknowingly approve an attacker's device during a completely...

Phishing Campaign Builds Fake Login Pages Inside Browsers After Trusted Microsoft Redirects
A phishing campaign chains DocuSign-themed calendar invitations, Microsoft redirects and browser blob URLs to display credential-stealing pages assembled in local memory. The method reduces reliance on a conventional...

N0va Phishing Kit Hijacks Real Microsoft Logins to Steal Session Tokens
A new phishing kit called N0va abuses legitimate device-code authentication flows for Microsoft, Google, and other trusted services to steal access and refresh tokens rather than passwords. The...
Phishing Campaign Chains Google Services to Conceal Credential Theft
A phishing operation is routing victims through legitimate Google services before sending them to personalized credential traps or unauthorized ScreenConnect installers. The technique weakens domain-reputation defenses and hides...
North Korea’s Kimsuky Hackers Turn to AI Coding Agents to Mass-Produce Phishing Lures
Genians researchers have linked a new Kimsuky campaign to the group's Operation GitPower cluster, revealing that the North Korean threat actor is now using an AI coding agent...
Phantom Deal Fraud Uses Fake M&A Secrecy to Push a €626,000 Wire Transfer
The Phantom Deal campaign impersonates executives and advisers, then uses a polished NDA to isolate employees from normal approval channels. One documented attempt sought a €626,735.45 transfer and...
QR-Code Phishing Reaches Record Levels as Attackers Shift Credential Theft to Phones
ESET says QR-code phishing accounted for about 11% of detected phishing email in the first half of 2026, with roughly 100,000 detections per month. By moving victims from...
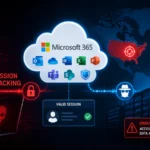
Microsoft 365 Session Hijacking Campaigns Hide Behind Trusted Remote-Support Tools
Campaigns spanning the United States and Europe are combining adversary-in-the-middle phishing with legitimate remote-management software. Stolen session cookies can outlive password resets, forcing defenders to revoke tokens and...