A critical vulnerability in Mirai botnet: remote DoS exploit discovered
Recent investigations into the Mirai botnet have unveiled a significant remote denial-of-service (DoS) exploit, identified as CVE-2024-45163. This vulnerability was discovered within the source code of the Mirai...
E-commerce vulnerabilities exposed: the Magento skimmer incident
A recent cyberattack targeting Magento, a widely used e-commerce platform, has raised significant concerns within the cybersecurity community. Hackers have successfully injected a malicious skimmer into Magento stores,...
Vulnerabilities in Google’s Quick Share could lead to remote code execution
Recent findings have spotlighted significant security vulnerabilities in Google’s Quick Share, a file-sharing tool that works across Android, Windows, and Chrome OS devices. Identified as “QuickShell” by researchers...
Critical zero-day vulnerability in Microsoft Office: CVE-2024-38200
On August 8th, Microsoft revealed a significant zero-day vulnerability, tracked as CVE-2024-38200, affecting multiple versions of its Office suite with a CVSS score of 7.5. This information disclosure...
Nexera suffers $1.8 million breach amidst security vulnerabilities
Nexera, a blockchain infrastructure protocol known for its tokenization solutions, recently experienced a significant security breach that resulted in the theft of $1.8 million, as revealed by cybersecurity...
A vulnerability unveiled: the 0.0.0.0 threats to browser security
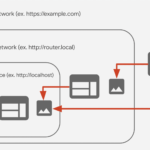
A recent study by Oligo Security has revealed a critical vulnerability impacting the world’s leading web browsers for the past 18 years. Dubbed the “0.0.0.0 Day” vulnerability, this...
Urgent security update: vulnerabilities addressed in Apache Linkis
Apache Linkis, a vital middleware for connecting applications to various data processing engines, has recently patched two significant security vulnerabilities affecting versions 1.3.2 to 1.5.0. These vulnerabilities pose...
Twilio discontinues Authy desktop service amidst investor pressures
Twilio has officially terminated its Authy desktop service, a move that will impact users who previously relied on the desktop application for multi-factor authentication. As of August 1,...