Docker Hub Token Transfer Flaw Exposed Trusted Images to Impersonation Risk
Docker fixed CVE-2026-105445, a critical token-ownership flaw that could make an attacker's personal access token authenticate as another user after account conversion. Docker found no evidence of abuse,...
Trojanized Terraform Provider Delivers Cross-Platform Backdoors to Developers
A malicious Terraform provider masquerading as an AWS plugin delivers FLATROOF and ROOFDECK malware across macOS, Linux, and Windows. The campaign targets developer and CI/CD environments where cloud...
Compromised Tensorlake npm Release Spreads Shai-Hulud Worm Through Developer Systems
A malicious Tensorlake npm release executed during installation, harvested developer and cloud secrets, and used worm-like techniques to threaten downstream projects. Teams that installed version 0.5.144 should treat...
Inside the Supply Chain Playbook Turning Trusted Software Updates Into Credential Thieves
A new ReversingLabs report ties together the S1ngularity, Shai-Hulud, and TeamPCP/Trivy supply chain incidents, showing how stolen maintainer tokens and compromised CI pipelines let attackers push credential-stealing code...
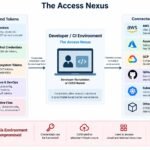
How a Single Poisoned Package Can Hand Attackers the Keys to Your Cloud
A new Qualys analysis ties together a string of 2025–2026 software supply chain campaigns — from the Shai-Hulud worm to malicious Ruby gems and Go modules — showing...
OpenCode Web Interface Flaw Let Hostile Sites Run Commands on Developer PCs
A flaw in OpenCode’s local web interface allowed a malicious website to turn an upgrade request into code execution on a developer machine. Version 1.18.22 fixes both the...
TanStack Supply-Chain Breach Exposes 170 Private CrowdSec Repositories
CrowdSec says attackers cloned roughly 170 private GitHub repositories after stealing an OAuth token through the TanStack npm supply-chain compromise. The incident remained hidden for months and highlights...
Critical Artifactory Bypass Is Being Used to Mint Administrator Tokens
A critical JFrog Artifactory authentication bypass is under active exploitation, with attackers reportedly creating administrator tokens on vulnerable servers. Self-hosted customers should upgrade immediately, revoke suspicious credentials and...