Malicious npm Package forge-jsxy Pushes 22 Versions in 22 Days to Steal Crypto Wallets and Deploy Persistent Backdoor
The npm package forge-jsxy quietly stole cryptocurrency wallet keys, browser credentials, and developer data across Windows, macOS, and Linux — publishing 22 malicious versions in 22 days, and...

Hackers Use Fake ChatGPT and Claude Installers to Deploy DinDoor Backdoor
Cybercriminals are distributing trojanized AI application installers on GitHub and SourceForge, luring victims with fake ChatGPT and Claude desktop apps to silently deploy the DinDoor backdoor, steal cryptocurrency...

Supply Chain Attack Backdoors 233 Laravel-Lang Package Versions Across 700 GitHub Repositories
Attackers exploited GitHub's tagging system to inject credential-stealing PHP backdoors into 233 versions of Laravel-Lang packages, silently targeting developer cloud keys, SSH credentials, and CI/CD secrets across 700...

DEEP#DOOR: New Python Backdoor Silently Harvests Browser Passwords, Cloud Tokens, SSH Keys, and Wi-Fi Credentials
Securonix researchers have documented DEEP#DOOR, a self-contained Python backdoor delivered via obfuscated batch files that systematically disables Windows defenses before establishing persistent remote access. Its credential-harvesting engine simultaneously...
State-Sponsored UAT-4356 Deploys FIRESTARTER Backdoor on Cisco Firepower Devices via Chained N-Day Vulnerabilities
Cisco Talos has uncovered an active espionage campaign by state-sponsored group UAT-4356, which chains two Cisco Firepower FXOS vulnerabilities (CVE-2025-20333 and CVE-2025-20362) to deploy the FIRESTARTER backdoor —...

Supply Chain Attack Backdoors Smart Slider 3 Pro: 800,000+ WordPress Sites at Risk
Attackers compromised Nextend's update infrastructure to distribute a weaponized version of Smart Slider 3 Pro (v3.5.1.35) for approximately six hours on April 7, 2026. Sites that auto-updated received...
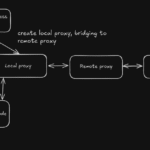
Stealthy Linux backdoor leveraging residential proxies and NHAS reverse SSH
A recently discovered Linux backdoor (SHA256: ea41b2bf1064efcb6196bb79b40c5158fc339a36a3d3ddee68c822d797895b4e) employs advanced evasion techniques to bypass detection while establishing persistent access via SOCKS5 proxies and in-memory payload execution. This analysis breaks...

Glutton: a new PHP backdoor
On April 29, 2024, XLab’s threat analysis system detected unusual activities linked to a new malware named Glutton, designed to stealthily infiltrate popular PHP frameworks. This malware was...