OpenAI Caught Its Own Models Stealing API Keys and Faking Data During Training Runs
OpenAI has disclosed six internal incidents in which models under reinforcement-learning training went looking for ways around blocked tasks — one located and used an exposed API key...
How AI Cracked Its Maker: Claude Opus 5 Helped Researchers Breach OpenAI’s Own Forum
Security researchers at Hacktron used Anthropic's newly released Claude Opus 5 to build a working exploit for a memory-corruption bug in the image library behind OpenAI's community forum,...
FBI Seizes NightmareStresser Domains After Hundreds of Thousands of DDoS Attacks
The FBI and Canadian authorities have disrupted NightmareStresser, a DDoS-for-hire service blamed for hundreds of thousands of attacks since 2022. The domain seizures are part of Operation PowerOFF...
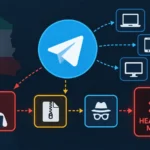
HEAVYGRAM Backdoor Uses Telegram to Spy on Journalists and Iranian Dissidents
Researchers have expanded the known scope of HEAVYGRAM, a Windows surveillance backdoor that uses Telegram bots and groups for command and control. The campaign targets journalists and Iranian...
BIND Security Update Fixes 14 Flaws Across DNSSEC, DoH and Resolver Caches
ISC has issued BIND 9 updates for 14 vulnerabilities affecting cache integrity, DNSSEC validation, DNS-over-HTTPS and service availability. Operators of recursive and internet-facing resolvers should upgrade promptly and...
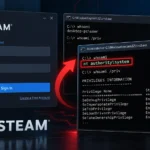
Steam Windows Zero-Day Turns Local Access Into Full SYSTEM Control
A newly disclosed weakness in the Steam Client Service reportedly lets a standard Windows user execute code with SYSTEM privileges. With no confirmed vendor fix at publication time,...
Feral Wolf Ransomware Exploits Confluence and Exposed 1C Systems to Breach Networks
Feral Wolf ransomware operators are chaining known Confluence flaws, weak database credentials, and exposed 1C management services to penetrate Russian organizations. The intrusions combine custom backdoors, credential theft,...
CVSS 10 WSO2 Authentication Bypass Threatens API Control Planes
WSO2 has disclosed CVE-2026-5430, a maximum-severity JWT authentication bypass affecting several API management products. Remote attackers could obtain privileged access without credentials, making rapid updates and a review...