Microsoft Sets Hard Deadline to Kill SMS and Voice Login Codes in Entra ID, Pushes Passkeys Instead
Microsoft is moving to make passkeys the default sign-in method across Entra ID while permanently retiring native SMS and voice-based multi-factor authentication by February 2027. The company says...
Stolen Azure Logins Expose Employee Data at McDonald’s, Vodafone and Seven Other Global Firms
A dark-web seller known as TheHatman is offering internal employee directories lifted from nine Fortune 500 companies, including McDonald's and Vodafone, after harvesting Azure Active Directory credentials through...
Legacy VNC Login on macOS Screen Sharing Could Hand Attackers a Root Shell
Researchers found that macOS's Screen Sharing service kept its file-transfer helpers running as root even when a session was authenticated with nothing more than a shared VNC password....
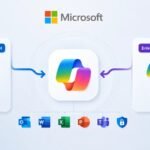
Microsoft Is Merging Consumer and Enterprise Copilot — Security Teams Should Watch the Seams
Microsoft is consolidating its consumer and business Copilot apps into a single Microsoft 365 Copilot experience, reachable from a unified m365.cloud.Microsoft address. Microsoft insists personal and organizational data...
AWS Sets a Multi-Year Countdown to Kill Off Email-Based Certificate Validation
Amazon is phasing out email validation for public TLS certificates issued through AWS Certificate Manager, with new-Region restrictions starting in 2027 and a full industry-wide browser distrust deadline...
Citrix NetScaler Root-Level RCE Flaw Goes Public With Working Exploit Code
A publicly released proof-of-concept shows how a pre-authentication heap overflow in Citrix NetScaler ADC and Gateway can be turned into unauthenticated, root-level remote code execution. There is no...
‘Bring Your Own EDR’ Trick Turns SentinelOne Into a Bodyguard for Malware
DEF CON 34 research shows how trusted SentinelOne components could be abused to dump memory from Windows' most protected processes, ultimately shielding malicious payloads behind the endpoint agent's...
Five New TP-Link Flaws Let Attackers Hijack ISP-Managed Routers and Mesh Systems
TP-Link has disclosed five vulnerabilities affecting its carrier-supplied Aginet router, mesh, and modem lineup, the worst of which lets an attacker on the network bypass authentication entirely. Because...