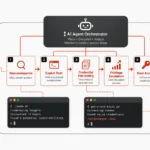
AI-Assisted Intruder Reaches Enterprise Root Access in Less Than 10 Hours
An attacker reportedly used frontier models and agentic frameworks to compress a complex enterprise intrusion into less than ten hours. The incident shows how exposed services, embedded secrets...
Microsoft Investigates Windows Teams Startup Failures as Users Turn to Web and Mobile
Some Windows users are seeing Microsoft Teams fail to open or take up to two minutes to load. Microsoft is gathering client logs under incident TM1466820, while web...
ZTNA in 2026: Ten Platforms Shaping Secure Access Beyond the Traditional VPN
A new 2026 market overview compares ten prominent zero-trust network access platforms for cloud, hybrid and remote environments. Buyers should look beyond feature checklists and test identity, device...
Security Teams Face a Week of Zero-Days, Router Intrusions and AI-Accelerated Attacks
A packed week of security disclosures combined active browser and commerce exploitation with router espionage, identity failures and faster AI-assisted intrusions. Defenders should use the converging signals to...
CrowdStrike Unveils SafeMind Agents to Pit Automated Defense Against AI-Driven Attacks
CrowdStrike has introduced SafeMind, a purpose-built family of offensive and defensive AI models designed around Falcon telemetry and incident-response knowledge. The company says the system can improve detection...
Critical ASUS Control Center Chain Opens Managed Fleets to Root Takeover
A CVSS 10.0 flaw chain in ASUS Control Center Enterprise can reportedly give an unauthenticated network attacker a root shell and control of centrally managed devices. Organizations should...
MikroTik RouterOS Flaw Under Active Attack Grants Unauthenticated Shell Access
Attackers are exploiting a RouterOS weakness that can reportedly provide unauthenticated shell access through exposed services, including SSH. MikroTik users should install the fixed releases now, audit every...
Bimbo Bakeries Employee Data Stolen Through Oracle EBS Zero-Day
Bimbo Bakeries USA says attackers obtained employee names and Social Security numbers through a vendor’s vulnerable Oracle E-Business Suite environment. The disclosure connects another major organization to a...