Antino Backdoor Hides Its Entire Command Channel Inside Microsoft 365
A China-linked espionage campaign has deployed a Rust backdoor whose native command-and-control workflow runs through Outlook and OneDrive. Cisco Talos found roughly 350 compromised endpoints across eight countries,...
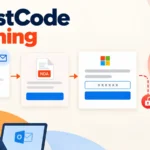
Inside GhostCode: The Phishing Kit That Turns MFA Approval Into Account Takeover
A newly identified phishing kit called GhostCode hijacks Microsoft 365 accounts by abusing the OAuth device-code sign-in flow, letting victims unknowingly approve an attacker's device during a completely...
Microsoft Investigates Windows Teams Startup Failures as Users Turn to Web and Mobile
Some Windows users are seeing Microsoft Teams fail to open or take up to two minutes to load. Microsoft is gathering client logs under incident TM1466820, while web...
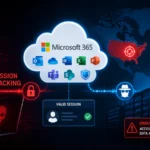
Microsoft 365 Session Hijacking Campaigns Hide Behind Trusted Remote-Support Tools
Campaigns spanning the United States and Europe are combining adversary-in-the-middle phishing with legitimate remote-management software. Stolen session cookies can outlive password resets, forcing defenders to revoke tokens and...
Mirage2FA Phishing Kit Hijacks Microsoft 365 Sessions at 3,500+ Organizations, Sidestepping MFA Entirely
A phishing-as-a-service kit called Mirage2FA has compromised thousands of Microsoft 365 accounts by stealing live session cookies through an adversary-in-the-middle proxy, letting attackers walk past passwords and MFA...
How One Phishing Email Let Attackers Bypass MFA and Redirect a Company’s Vendor Payments
An HR-themed phishing lure led a finance employee to a fake Microsoft 365 login that stole an authenticated session cookie, letting attackers bypass MFA entirely. Over the following...

Microsoft Is Merging Consumer and Enterprise Copilot — Security Teams Should Watch the Seams
Microsoft is consolidating its consumer and business Copilot apps into a single Microsoft 365 Copilot experience, reachable from a unified m365.cloud.Microsoft address. Microsoft insists personal and organizational data...

New Outlook Flaw Lets Attackers Run Malicious Code Through a Single Booby-Trapped Email Attachment
Microsoft has patched a high-severity remote code execution flaw in Outlook, tracked as CVE-2026-70329, that can be triggered when a victim opens a specially crafted Office file. The...