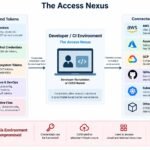
How a Single Poisoned Package Can Hand Attackers the Keys to Your Cloud
A new Qualys analysis ties together a string of 2025–2026 software supply chain campaigns — from the Shai-Hulud worm to malicious Ruby gems and Go modules — showing...
OpenCode Web Interface Flaw Let Hostile Sites Run Commands on Developer PCs
A flaw in OpenCode’s local web interface allowed a malicious website to turn an upgrade request into code execution on a developer machine. Version 1.18.22 fixes both the...
TanStack Supply-Chain Breach Exposes 170 Private CrowdSec Repositories
CrowdSec says attackers cloned roughly 170 private GitHub repositories after stealing an OAuth token through the TanStack npm supply-chain compromise. The incident remained hidden for months and highlights...
Critical Artifactory Bypass Is Being Used to Mint Administrator Tokens
A critical JFrog Artifactory authentication bypass is under active exploitation, with attackers reportedly creating administrator tokens on vulnerable servers. Self-hosted customers should upgrade immediately, revoke suspicious credentials and...

Malicious NuGet Package Impersonates Sicoob Banking SDK to Steal mTLS Certificates and Financial Credentials
A malicious NuGet package named "Sicoob.Sdk" impersonated the official Sicoob banking SDK and silently exfiltrated PFX certificates, private keys, and banking credentials from 484 downloads using Sentry telemetry...