Stolen Azure Logins Expose Employee Data at McDonald’s, Vodafone and Seven Other Global Firms
A dark-web seller known as TheHatman is offering internal employee directories lifted from nine Fortune 500 companies, including McDonald's and Vodafone, after harvesting Azure Active Directory credentials through...
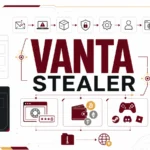
New Vanta Stealer Malware Raids Browsers, Crypto Wallets and Gaming Accounts in a Single Sweep
A newly documented information stealer called Vanta Stealer goes well beyond saved browser passwords, harvesting cookies, payment data, Discord tokens, gaming accounts and cryptocurrency wallet files in one...
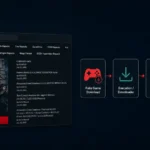
Fake Game Downloads Are Quietly Installing Amatera Stealer Through a Disguised RenPy Loader
A malware campaign is hiding behind fake games, cracks, and mods to install Amatera Stealer, a multi-stage infostealer that harvests browser credentials, messaging data, and cryptocurrency wallets. The...
PamStealer: New macOS Infostealer Disguises Itself as the Maccy Clipboard Manager
PamStealer is a newly discovered macOS infostealer that impersonates the Maccy clipboard manager, using a two-stage AppleScript-to-Rust infection chain to steal Keychain data, browser credentials, and clipboard contents...
Operation Endgame Strikes Again: Europol Seizes StealC, Amadey and SocGholish Infrastructure — 326 Servers Down, $47M Frozen
Europol's Operation Endgame has dismantled the infrastructure behind StealC, Amadey, and SocGholish malware, seizing 326 servers, freezing USD 47 million in crypto, and recovering 27 million stolen credentials....
Supply Chain Attack Compromises 140+ Mastra npm Packages, Targeting Developer Credentials and Crypto Wallets
A sophisticated supply chain attack has compromised over 141 packages in the Mastra-AI npm ecosystem, including @mastra/core which sees 918,000 weekly downloads. Detected on June 17, 2026, the...
GoFlateLoader: New Go-Based Malware Loader Infects 33,000+ Users by Outsizing Security Scanners
GoFlateLoader, a new Go-based malware loader active since April 2026, has infected over 33,000 users globally by exploiting a simple but effective trick: inflating its file size to...
Gremlin Stealer Evolves: New Variant Hides C2 URLs in Encrypted Resources and Adds Discord Token Theft
A newly analyzed Gremlin stealer variant hides C2 URLs inside XOR-encrypted .NET resource sections, making it invisible to static scanners. The malware now targets Discord tokens and adds...