Uncensored Local AI Reworks Credential Dumper to Evade Two EDR Platforms
A controlled experiment showed a locally hosted, guardrail-free AI model modifying an LSASS credential dumper until it escaped detection by two unnamed EDR products. The limited test does...
Console Pipe Injection Shows Why EDR Cannot Rely on Classic Memory-Write Signals
A newly disclosed Windows injection method delivers payload bytes through a child console process’s redirected input, avoiding two APIs commonly associated with remote code injection. The technique still...
ClearFake CAPTCHA Campaign Disables EDR to Deploy Crypto Stealer
ClearFake has expanded its fake CAPTCHA operation with a vulnerable-driver technique that terminates endpoint defenses before deploying a cryptocurrency stealer. The campaign combines compromised sites, blockchain-hosted instructions, WebDAV...

‘Bring Your Own EDR’ Trick Turns SentinelOne Into a Bodyguard for Malware
DEF CON 34 research shows how trusted SentinelOne components could be abused to dump memory from Windows' most protected processes, ultimately shielding malicious payloads behind the endpoint agent's...
GentleKiller: Inside the Ransomware Framework Disabling 400+ EDR Security Products
ESET researchers have exposed GentleKiller, the in-house EDR-killing framework of the Gentlemen ransomware gang, capable of disabling over 400 security processes across 48 products using BYOVD kernel driver...

SilentButDeadly: a targeted disruption of EDR networks
The relentless evolution of cyber threats has forced security professionals to continually adapt, often relying on increasingly complex Endpoint Detection and Response (EDR) solutions. However, this reliance introduces...
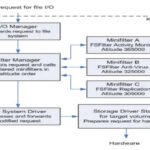
Windows MiniFilter vulnerability: a threat to EDR security
Endpoint Detection and Response (EDR) solutions are essential for modern cybersecurity defenses. However, research has revealed a vulnerability in Windows MiniFilter drivers that can be exploited to prevent...