GhostAction Hijacks 346 GitHub Repositories to Harvest CI/CD Secrets
The GhostAction campaign used compromised maintainer accounts to inject credential-stealing GitHub Actions workflows into 346 repositories. The malicious automation collected CI/CD secrets and searched full Git histories, creating...
GitLab’s Email-to-Issue Feature Can Be Hijacked to Commit Code as Any User
Researchers at Aikido Security found that GitLab’s incoming-email work-item feature relies on a long-lived, non-expiring token that, if exposed, lets an attacker submit merge requests and land commits...
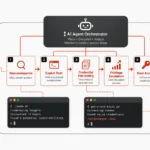
AI-Assisted Intruder Reaches Enterprise Root Access in Less Than 10 Hours
An attacker reportedly used frontier models and agentic frameworks to compress a complex enterprise intrusion into less than ten hours. The incident shows how exposed services, embedded secrets...
Unauthenticated RCE Flaw in JetBrains TeamCity Puts Software Supply Chains at Risk
JetBrains has patched a critical, unauthenticated remote code execution flaw (CVE-2026-63077) in TeamCity On-Premises that could let attackers hijack build servers and tamper with software releases. Administrators are...
Microsoft Warns: Claude Code GitHub Action Exploitable via Prompt Injection to Leak CI/CD Secrets
Microsoft Threat Intelligence disclosed a prompt injection flaw in the Claude Code GitHub Action that allowed attackers to access /proc/self/environ and steal API keys from CI/CD runners. Anthropic...