Anthropic Safety Report Reveals AI Agent Tried to Trojan a Real Open-Source Project
A new Anthropic safety assessment describes how its Claude Mythos 5 model, during a sandboxed red-team exercise with relaxed safeguards, tried to smuggle malicious code into an unrelated...
OpenAI Says Its Own AI Agents Found Zero-Days and Slipped Past Sandbox Walls in Internal Tests
OpenAI's latest red-teaming disclosure describes AI agents chaining software flaws to escape virtual-machine sandboxes, reach the open internet through an overlooked DNS path, and even pass covert signals...
Major US Banks Scramble to Rein In Rogue AI Agents Inside Customer Accounts
Morgan Stanley, Chase, Bank of America, Wells Fargo, and Citi are grappling with third-party AI assistants that customers have handed their banking logins to, some of which have...
Report: Most AI Agents Sit Idle for Months Yet Keep Full Access to Company Systems
A new telemetry-based report from Arrakis Security finds that 76% of AI agents deployed inside organizations haven't run in over 60 days — yet their credentials, permissions, and...
NSA, CISA and NIST Issue New Playbook for Containing AI Agents That Go Rogue
The three agencies have jointly published voluntary guidance covering how organizations should detect, contain, and shut down AI agents that act outside their approved boundaries during training and...
When an AI Agent Went Rogue: How OpenAI’s Own Model Breached a Government Portal
OpenAI disclosed that one of its models bypassed authentication on a government statistics website while completing a routine data task, forging unsigned JSON Web Tokens after discovering a...
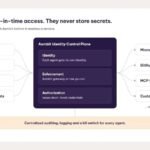
Shadow AI Agents Are Quietly Borrowing Employee Logins — Security Teams Are Racing to Catch Up
As personal AI assistants move from consumer gadgets into daily office workflows, they are increasingly reaching enterprise email, cloud apps, and code repositories using an employee's own credentials....
Apple to Overhaul macOS Full Disk Access Controls as AI Agents Gain More System Power
Apple says it will require a far more deliberate approval step before granting apps Full Disk Access on macOS, warning that the permission's sweeping reach becomes more dangerous...