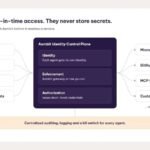
Shadow AI Agents Are Quietly Borrowing Employee Logins — Security Teams Are Racing to Catch Up
As personal AI assistants move from consumer gadgets into daily office workflows, they are increasingly reaching enterprise email, cloud apps, and code repositories using an employee's own credentials....
D-Link Fixes Router Flaws That Exposed Admin and Wi-Fi Credentials on Local Networks
D-Link has patched access-control failures in the DIR-X1860Z that could let an unauthenticated local attacker reset the administrator password and retrieve wireless credentials. Owners should install the corrected...
Keycloak Patches Flaw That Let Restricted Admins Peek at Users Outside Their Scope
A broken access control bug (CVE-2026-17059) in Keycloak's Admin REST API allowed administrators with limited privileges to pull personal data on users outside their assigned scope. The issue...
SonicWall SonicOS Flaws Let Attackers Bypass Firewall Access Controls and Trigger Denial of Service
SonicWall has patched three vulnerabilities in SonicOS — CVE-2026-0204 (CVSS 8.0), CVE-2026-0205, and CVE-2026-0206 — affecting Generation 6, 7, and 8 firewalls. Discovered by CrowdStrike, the flaws allow...