South Korean Church Breaches Expose More Than One Million Congregant Records
Attackers penetrated two major South Korean churches through a web shell, leaked credentials and broken authorization controls, exposing records tied to more than one million congregants. The intrusions...
CyberXero Uses AI Agent Swarms to Scale WordPress Intrusions and Target Ukrainian Energy
A Russian-speaking initial-access broker known as CyberXero used dozens of AI agents alongside PentAGI and Cobalt Strike to automate web attacks and conduct targeted reconnaissance. Exposed operator files...
Attackers Hijack Three Country-Code Registries to Obtain Rogue HTTPS Certificates
Attackers compromised the .gh, .sl and .as domain registries and exploited DNS control to obtain unauthorized HTTPS certificates for Google and other organizations. Chrome blocked known certificates, but...
SonicWall Fixes Maximum-Severity SMA1000 Flaw Allowing Pre-Login Internal Requests
SonicWall has patched four SMA1000 vulnerabilities, led by a CVSS 10 pre-authentication SSRF flaw that can turn an exposed appliance into a proxy for internal requests. Organizations must...
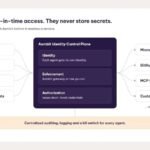
Shadow AI Agents Are Quietly Borrowing Employee Logins — Security Teams Are Racing to Catch Up
As personal AI assistants move from consumer gadgets into daily office workflows, they are increasingly reaching enterprise email, cloud apps, and code repositories using an employee's own credentials....
Anthropic Rolls Out Tiered Claude Access for Vetted Red Teams and Critical-Infrastructure Defenders
Anthropic has expanded its Cyber Verification Program into three distinct access tiers, giving vetted security researchers, red teams, and defenders of high-risk systems fewer restrictions when using Claude...
Fired IT Admin Gets 32 Months for Bitcoin Extortion Plot That Nearly Crippled a New Jersey Company’s Network
Daniel Rhyne, a former core infrastructure engineer, has been sentenced to 32 months in federal prison for planting a hidden virtual machine, deleting domain administrator accounts, and demanding...
ASOS Investigates Breach After Hackers Hijack App Notifications to Issue Public Ransom Threat
Online fashion retailer ASOS is investigating an incident after attackers abused a third-party customer communication platform to push a fake "ASOS HACKED" push notification claiming access to its...