
China-Linked APTs exploit critical SAP NetWeaver vulnerability to breach over 580 systems globally
In a significant escalation of cyber-espionage activities, multiple China-affiliated advanced persistent threat (APT) groups have been found actively exploiting a recently disclosed critical vulnerability in SAP NetWeaver, identified...
JPEG image FUD ransomware: a way to evades antivirus solutions
In a concerning development for cybersecurity professionals, threat actors have begun leveraging a novel Fully UnDetectable (FUD) ransomware attack technique that utilizes seemingly benign JPEG image files as...
New malware LOSTKEYS uncovered in COLDRIVER campaign targeting Western governments and NGOs
The Google Threat Intelligence Group (GTIG) has recently uncovered a sophisticated new malware strain, dubbed LOSTKEYS, deployed by the Russian state-sponsored threat actor COLDRIVER (also known as UNC4057,...

German authorities shut down major crypto-swapping platform “eXch,” seizing €34 million in illicit assets
On April 30, 2025, the Frankfurt am Main General Prosecutor’s Office-Central Unit for Combating Internet Crime (ZIT)-in close collaboration with the German Federal Criminal Police Office (BKA), executed...
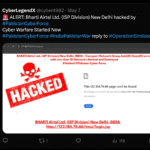
Tactical reality behind the India-Pakistan hacktivist surge
In May 2025, a wave of hacktivist activity targeting Indian digital infrastructure sparked widespread alarm in media and social networks, with numerous groups claiming significant breaches of government,...
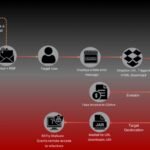
From PDF invoice to geo-fenced RAT delivery campaign
A recent campaign targeting Southern European organizations demonstrates advanced evasion techniques combining social engineering, trusted platforms, and geolocation filtering. The attack chain unfolds through four precision stages: 1....
Emerging DOGE Big Balls ransomware campaign leverages multi-stage tooling and BYOVD exploits
A recent analysis of newly discovered payloads linked to the DOGE Big Balls ransomware operation reveals a complex infection chain combining open-source tools, kernel-level exploits, and psychological warfare....

Malicious npm packages hijack macOS Cursor AI IDE
The Socket Threat Research Team has uncovered a sophisticated supply chain attack targeting macOS developers using the Cursor AI code editor. Three malicious npm packages-sw-cur, sw-cur1, and aiide-cur-have...