FBI Seizes NightmareStresser Domains After Hundreds of Thousands of DDoS Attacks
The FBI and Canadian authorities have disrupted NightmareStresser, a DDoS-for-hire service blamed for hundreds of thousands of attacks since 2022. The domain seizures are part of Operation PowerOFF...
CISA’s Latest Advice for Defenders: Lay Traps for Hackers Before They Even Get In
CISA has published new guidance urging organizations to seed their networks with fake credentials, decoy systems and honeytokens so that any attacker who slips past perimeter defenses trips...
How a Hijacked Thai College Webpage Became a Funnel Into an Illegal Online Casino
Fraud investigators at ADEX traced suspicious ad traffic back to a compromised page on a Thai academic institution's website that Google had indexed and ranked highly, then quietly...

Luciferus Markets Subscription AI for Malware Development on Criminal Forums
A service called Luciferus is being promoted on an underground forum as an unrestricted AI assistant for malware-related requests. Researchers confirmed its willingness to generate RAT code, but...
FortiGate Exploit Opens Broadband Provider to Credential Theft and Network Pivoting
Researchers uncovered infrastructure indicating that attackers exploited a FortiGate SSL-VPN weakness during an intrusion targeting Thailand’s 3BB broadband provider. The operation combined perimeter access, privilege escalation, credential theft...
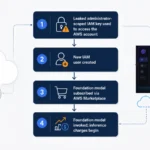
Leaked AWS Administrator Key Fuels Costly LLMjacking Through Bedrock and Marketplace
A leaked AWS IAM key with administrator privileges allowed an attacker to create a new identity, activate premium AI models and bill inference usage to the victim. The...
BREEZE COMET Hackers Use AI-Written Tools to Speed-Run Brazilian Bank Fraud
Google Cloud researchers detail how the financially motivated BREEZE COMET group has spent two years infiltrating Brazilian banks and retailers, combining social engineering and rogue hardware with generative-AI-assisted...
Cyber Incident Halts Small UK Power Plant for Four Days as Attribution Remains Unclear
A cyber incident reportedly stopped a small British peaking power plant for roughly four days without disrupting customers or the wider grid. Officials confirmed the event, while key...