AWS Closes an SSRF Hole in Its MCP Gateway That Could Turn a Trusted User Into an Internal Network Scanner
AWS has patched a server-side request forgery flaw in its open-source mcp-gateway-registry project, tracked as CVE-2026-125926, that let an authenticated user with server-registration rights redirect the gateway to...
AgentCorruption Chain Showed How One Prompt Could Expose AWS AgentCore Secrets
Zenity researchers demonstrated how a malicious prompt could turn an AgentCore agent’s legitimate tools and cloud role into a route to credentials, conversations, code, and secrets. AWS has...
Leaked Control Panel Exposes 50,000 Stolen Credentials Harvested From WordPress Backups
Researchers at LevelBlue uncovered TIKTOUK, a credential-harvesting toolkit that scans for exposed WordPress backups, configuration files, and JavaScript secrets. A leaked operator panel contained roughly 50,000 real credentials...
AWS Integration Lambda Could Turn Limited IAM Access Into Privileged Cloud Actions
CVE-2026-94384 allowed callers of an Amazon Connect Salesforce setup function to make AWS requests with the Lambda execution role's privileges. AWS has fixed the issue in AmazonConnectSalesforceLambda 5.26...
Mass Scanning of Exposed Vite Servers Targets AWS and Azure Secrets
Attackers are automatically probing internet-accessible Vite development servers for environment files, cloud credentials and infrastructure secrets. F5 telemetry recorded about 32,000 raw events in August, highlighting the risk...
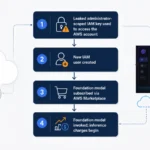
Leaked AWS Administrator Key Fuels Costly LLMjacking Through Bedrock and Marketplace
A leaked AWS IAM key with administrator privileges allowed an attacker to create a new identity, activate premium AI models and bill inference usage to the victim. The...
28,000 Public .git Folders Left AWS Keys, Stripe Tokens, and HR Files Wide Open, Researchers Find
A large-scale internet scan uncovered 28,000 publicly accessible .git directories exposing hundreds of live cloud and payment credentials, along with sensitive employee records — a reminder that scrubbing...

AWS Sets a Multi-Year Countdown to Kill Off Email-Based Certificate Validation
Amazon is phasing out email validation for public TLS certificates issued through AWS Certificate Manager, with new-Region restrictions starting in 2027 and a full industry-wide browser distrust deadline...