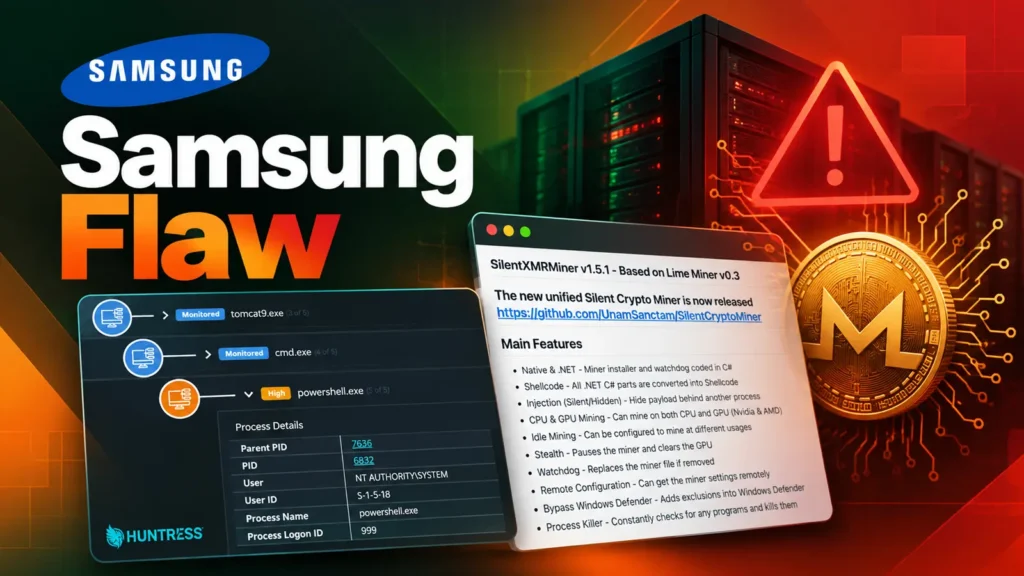
Attackers exploited a known vulnerability in Samsung MagicINFO Premium to compromise a Windows system, establish remote access and build a Monero cryptocurrency miner directly on the victim. The intrusion, investigated by Huntress in early September 2026, demonstrates how a neglected internet-facing flaw can support repeated access even after defenders respond to an initial alert.
MagicINFO is used to manage digital-signage deployments. Investigators traced the activity to CVE-2025-4632, a file-write vulnerability that can place attacker-controlled content on a server with system privileges. Samsung issued a fix in May 2025 after an earlier MagicINFO weakness, CVE-2024-7399, was incompletely remediated.
Attackers returned through the same opening
Huntress first alerted the affected customer and provided remediation guidance. Eight days later, analysts observed new malicious activity tied to the same route, indicating that the vulnerable service could still be reached. The public report describes one managed endpoint rather than a measured campaign across many organizations, but its sequence offers a useful picture of post-exploitation behavior.
The intruders attempted three times to retrieve AnyDesk, a legitimate remote administration tool frequently abused for unauthorized persistence. A Windows download utility was used first, followed by PowerShell; Microsoft Defender blocked both efforts. A third method succeeded, and the attackers configured a password to enable later connections. Process ancestry led back to the MagicINFO service, connecting the remote tool to exploitation of the application.
They then created a local administrator account and reused the AnyDesk password for it. The operators also invoked a Windows settings component to disable Microsoft Defender. Together, those actions increased their options for returning to the host and reduced the chance that subsequent tools would be stopped.
The miner was assembled on the victim
Instead of downloading a finished mining executable, the attackers launched a Silent XMR Miner builder from the new user’s Documents directory. The builder spawned multiple Windows development utilities and C compilers. Compiling locally may help tailor a payload to the target and avoid simple reputation checks against a known binary.
That technique also created a conspicuous behavioral trail. An unsigned builder launching a burst of compiler processes on a signage management server is unusual, giving endpoint monitoring a detection opportunity before mining begins. Analysts later observed connections to a public Monero pool, apparently consuming the system’s CPU and potentially its graphics resources. Mining activity appeared beneath Windows Explorer, another sign that code was running where it did not belong.
The immediate cost is stolen computing capacity, but the larger risk comes from system-level file placement, weakened antivirus controls, a new administrator and persistent remote access. An operator with those capabilities could deploy a different payload, steal data or use the server as a foothold into nearby systems.
What defenders should check
Organizations using MagicINFO should confirm that every internet-reachable installation includes Samsung’s correction for CVE-2025-4632. They should also determine whether the service was exposed before patching and investigate for post-exploitation artifacts rather than assuming an update alone removes an existing intruder.
- Review MagicINFO service process trees for command shells and download utilities.
- Investigate unexpected AnyDesk installation or password configuration.
- Look for newly created local administrators and unauthorized Defender changes.
- Alert on compiler toolchains launched from user folders or server applications.
- Examine outbound connections to mining pools and unexplained sustained CPU use.
Defenders should preserve logs and rotate credentials used on a compromised host. Reimaging may be safer than trying to remove individual tools when attackers have held system privileges. Network access for digital-signage management should also be restricted to trusted administration paths instead of exposing the service directly to the internet.
The central lesson is that deleting a miner treats the symptom, not the breach. Teams must close the initial vulnerability, remove persistence, validate accounts and security settings, and determine what the intruder could reach while the server was under external control.
Source: Cyber Security News.
Leave a Reply
You must be logged in to post a comment.