Attackers Exploit Critical Bricksforge Flaw to Run PHP on WordPress Sites
Attackers are actively exploiting a maximum-severity Bricksforge vulnerability to turn image uploads into executable PHP files. WordPress administrators should update immediately and inspect upload directories and request logs...
Crafted HEIC Uploads Can Turn WordPress Image Processing Into Server Code Execution
A newly demonstrated exploit chain turns a malicious HEIC upload into code execution through WordPress's server-side image pipeline. Administrators should update libheif, restrict unnecessary modern image formats, and...
Click2Shell Chain Turns One Malicious Link Into WordPress Server Takeover
WordPress has fixed a theme-preview weakness that can silently install an attacker-selected theme when an administrator opens a crafted link. Paired with unsafe pre-activation code in a theme,...
Two Critical Flaws in a Popular WordPress Calendar Plugin Put 600,000+ Sites at Risk of Full Takeover
Two unauthenticated, maximum-severity vulnerabilities in the widely used 'The Events Calendar' WordPress plugin could let attackers seize full control of more than 600,000 websites without ever logging in....
Unauthenticated File Upload Flaw in Elementor Pro Opens Door to Remote Code Execution
A critical vulnerability tracked as CVE-2026-32475 lets unauthenticated attackers upload malicious PHP files through the Elementor Pro Forms widget, potentially leading to full remote code execution on affected...
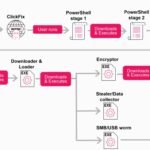
Fake CAPTCHA Prompts on Hacked WordPress Sites Fuel Global StopAndProtect Malware Botnet
Researchers have uncovered a sprawling campaign, dubbed StopAndProtect, that has hijacked thousands of poorly maintained WordPress sites to serve as rotating command-and-control infrastructure. Fake CAPTCHA prompts trick visitors...
New WordPress Flaw Turns a Failed Login Attempt Into Full Server Takeover
A newly disclosed WordPress vulnerability, dubbed XSS2Shell and tracked as CVE-2026-64638, chains a decade-old parsing quirk in the login page into full remote code execution, putting an estimated...

wp2shell: The WordPress Core Bug That Lets Anyone Take Over 500 Million Sites Without Logging In
A newly disclosed WordPress Core vulnerability, nicknamed wp2shell, chains a REST API batch-route flaw into full unauthenticated remote code execution. No plugins, no login, and no special configuration...